HackConRD CTF 2024: Firensics

This challenge tells us that an employee is suspected of having leaked confidential company data, and requires us to find sensitive information in some files provided.
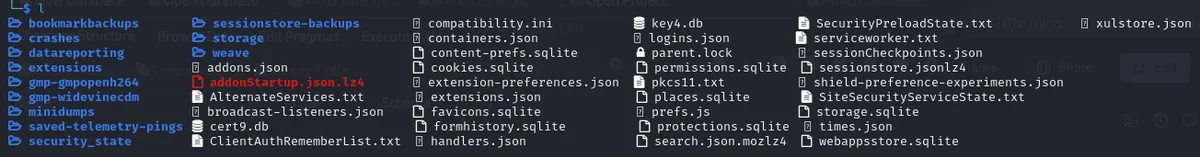
We got a zip file that included all the files and folders shown below. Taking a closer look and doing some research, we found that we have Firefox artifacts.
An artifact is a remnant or trace left behind on the computer which helps to identify the source of malicious traffic and attacks conducted on the system. A few examples include cache data, history, downloads, etc.
Firefox stores these artifacts inside specific folders in the operating system.
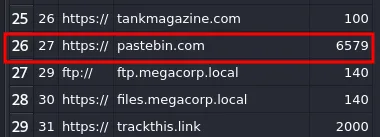
Browsing through all these files and after reviewing them, we found places.sqlite. Here we could find the moz_origins table, and we saw something particular: the pastebin.com website is the most visited of all, with 6579 visits. That is curious.
Pastebin.com is the number one paste tool since 2002. Pastebin is a website where you can store text online for a set period of time.
Moving to the moz_places table, we find a particular URL that takes us to a note saved on pastebin.com.
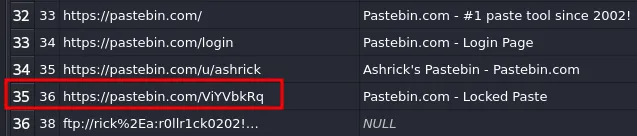
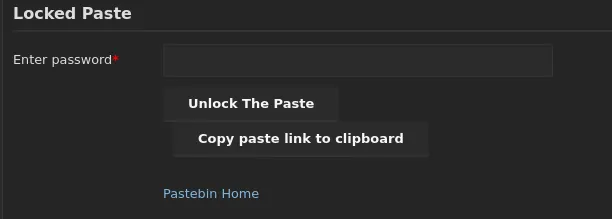
When we access this URL, we see that it requires a password to release the information.
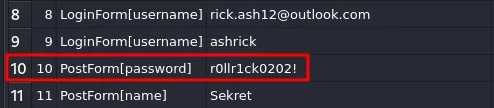
Searching a little, we found another database, formhistory.sqlite. In the moz_formhistory table we find a LoginForm[username] and a PostForm[password]. We try to use the password to release the data on pastebin.com.
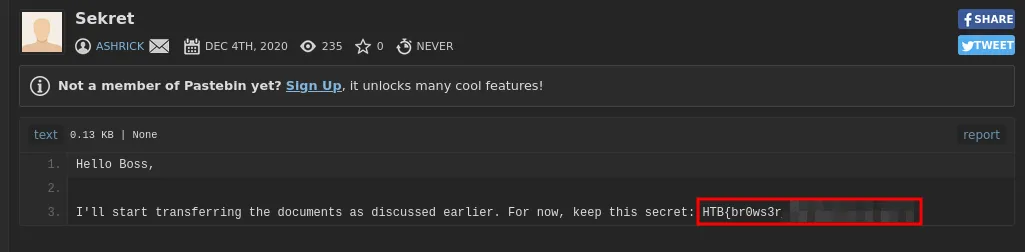
Accessing the note, we were able to obtain the flag.
Thanks for reading.