HackTheBox: Cozy Hosting
Cozy Hosting is an easy Linux machine: an exposed Spring Boot Actuator leaks a session cookie, an admin panel allows command injection bypassing whitespace with IFS, and sudo ssh gives root via GTFOBins.
Cozy Hosting is an easy Linux machine: an exposed Spring Boot Actuator leaks a session cookie, an admin panel allows command injection bypassing whitespace with IFS, and sudo ssh gives root via GTFOBins.
Analytics is an easy Linux machine: an unauthenticated Metabase RCE (CVE-2023-38646) lands us in a Docker container, environment variables leak SSH credentials, and GameOver(lay) gives root.
Keeper is an easy Linux machine: default credentials on a Request Tracker instance expose an SSH password, and a KeePass memory dump (CVE-2023-32784) plus a PuTTY key lead to root.
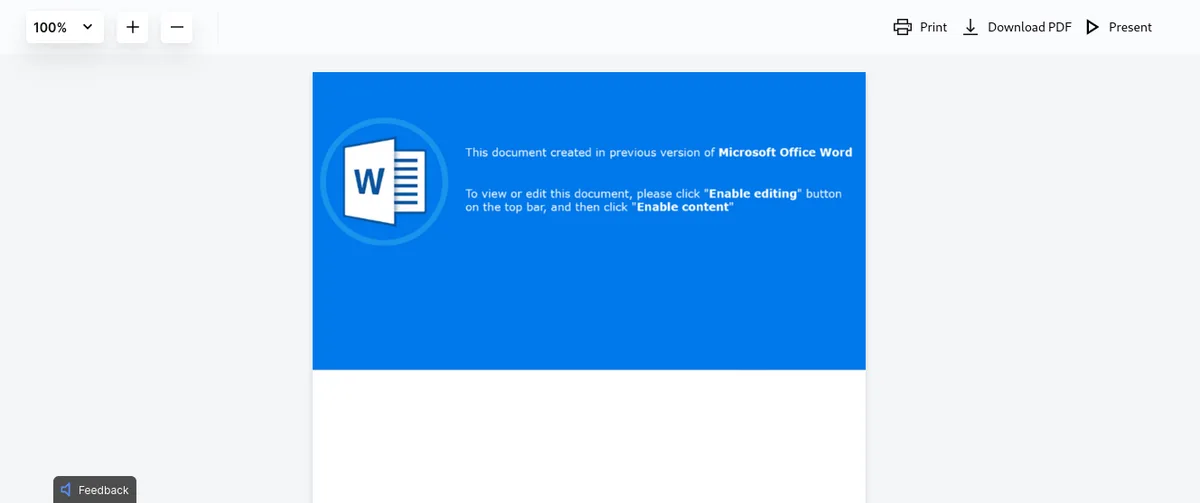
Forensics writeup: analyzing a malicious .docm with oletools (olevba) to extract a VBA macro and decode the obfuscated Chr()/ASCII payload that hides the flag.
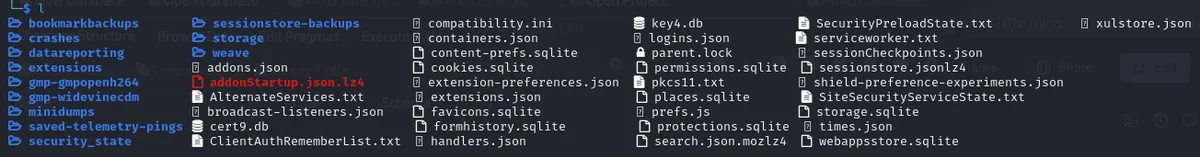
Forensics writeup: recovering a leaked flag from Firefox browser artifacts (places.sqlite and formhistory.sqlite) to unlock a password-protected Pastebin note.
Writeup of the Broken Production web challenge: forging an admin session from a Base64 cookie, bypassing an LFI filter with ....//, and turning it into RCE through log poisoning.